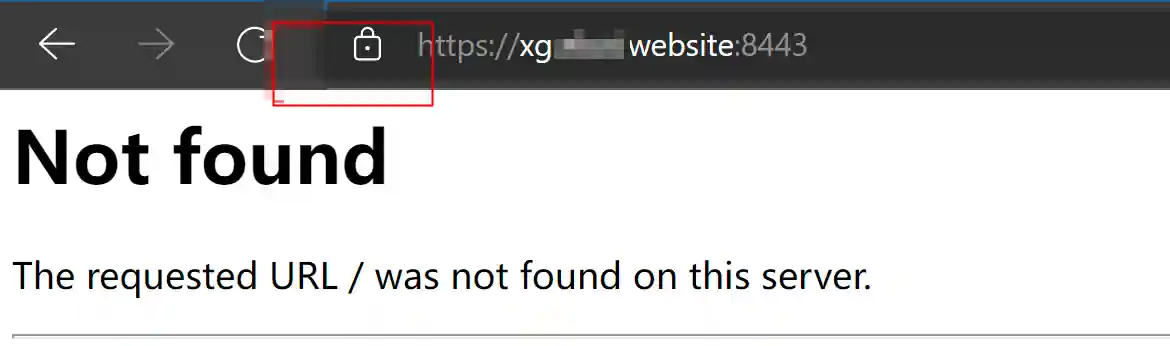
Monitoring Configuration of Legitimate SSL Certificates
Environment Preparation
- Ensure that Viper is running normally.
- The domain name configuration is correct and has been pointed to the IP address of Viper's VPS.

Obtaining Certificates
Here, acme.sh is used as an example to illustrate how to obtain legitimate certificates from letsencrypt.org.
- Install acme.sh

plain
curl https://get.acme.sh | sh -s [email protected]- Generate a certificate (ensure that port 80 is not occupied)

plain
acme.sh --issue -d xg.xxx.website --standalone
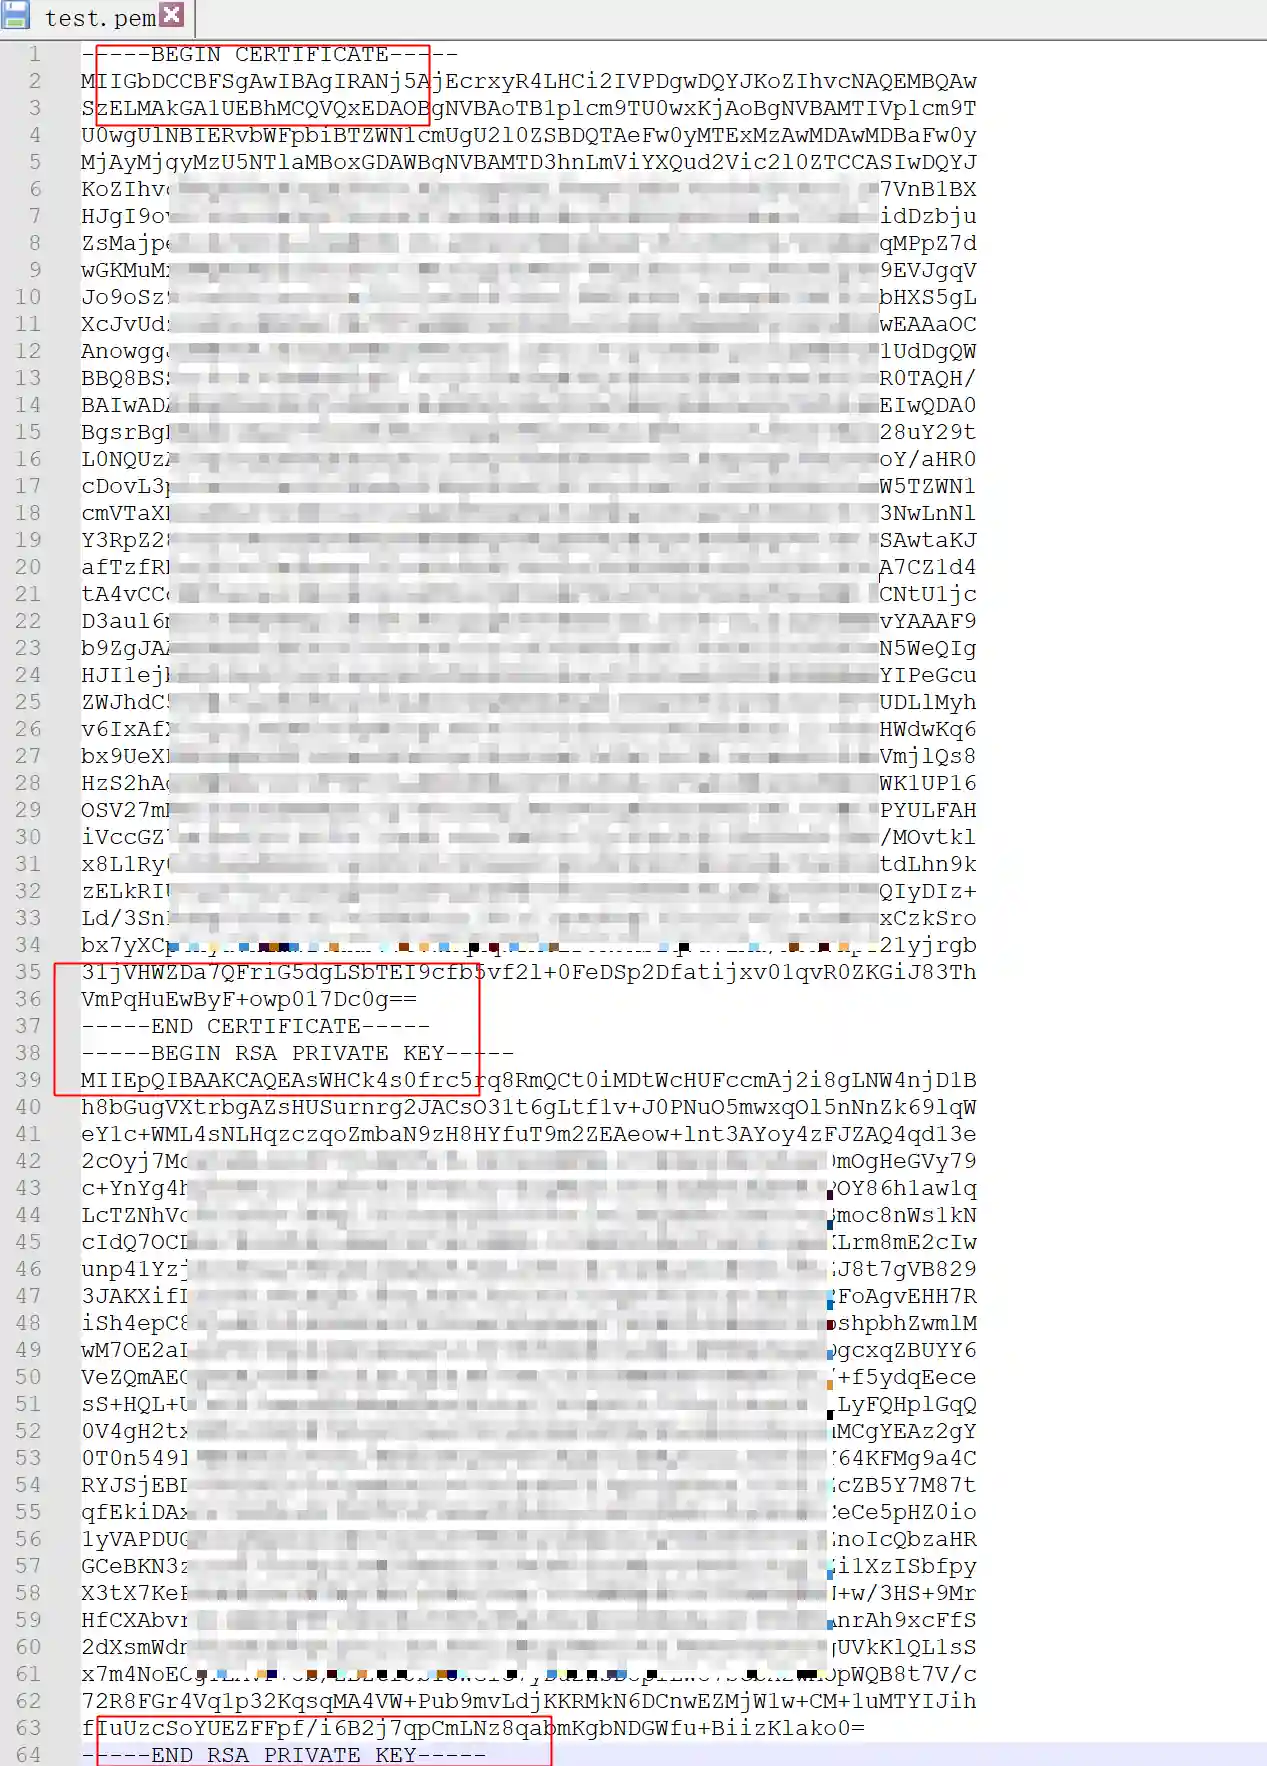
- Merge the contents of the xg.xxx.website.key and xg.xxx.website.cer files into one file.
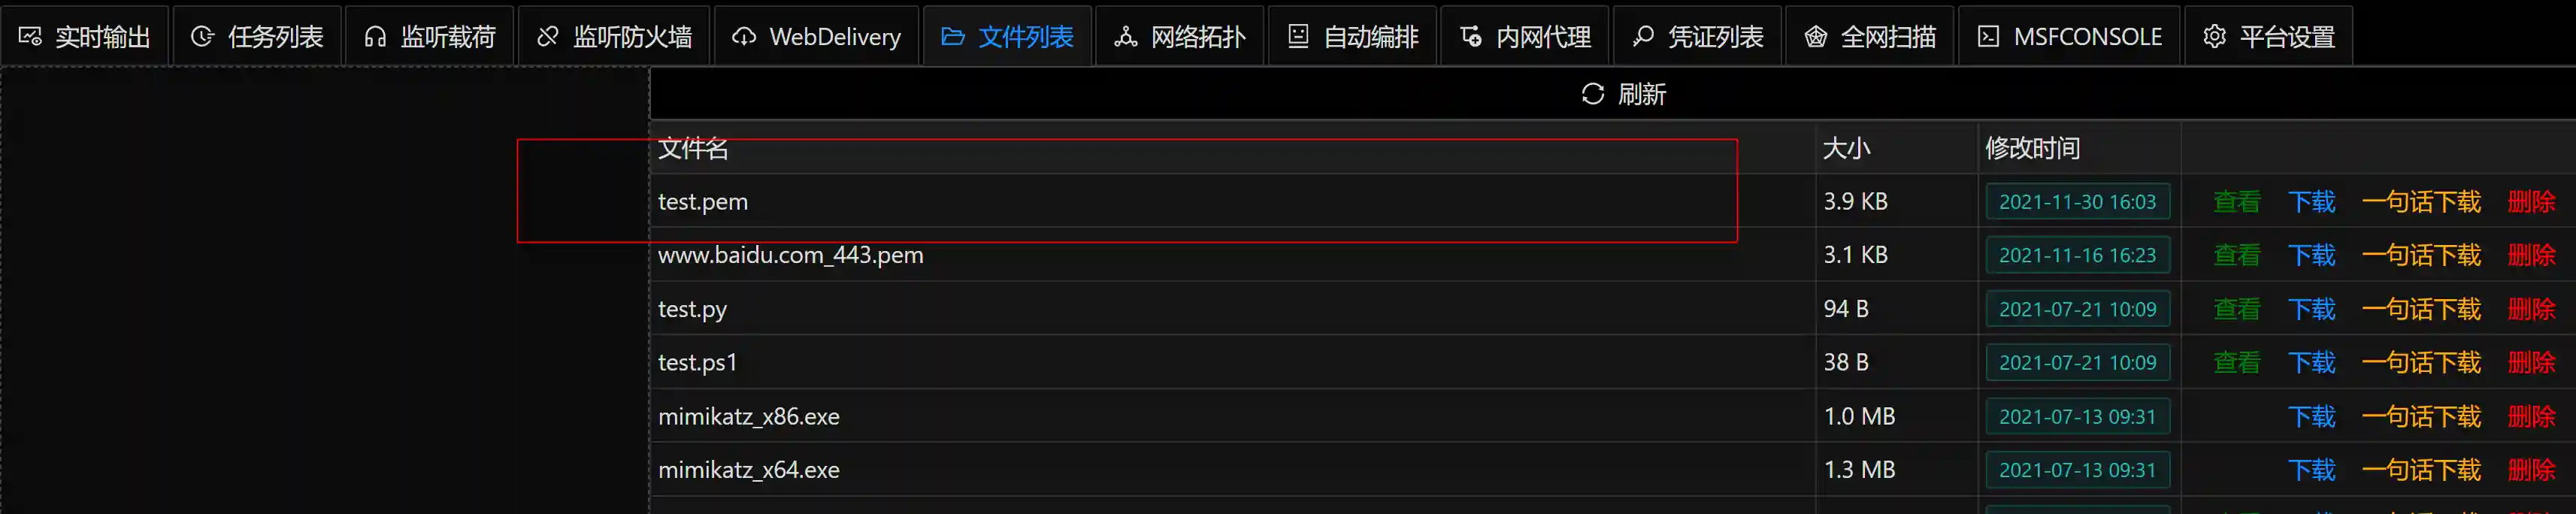
- Upload test.pem to viper.
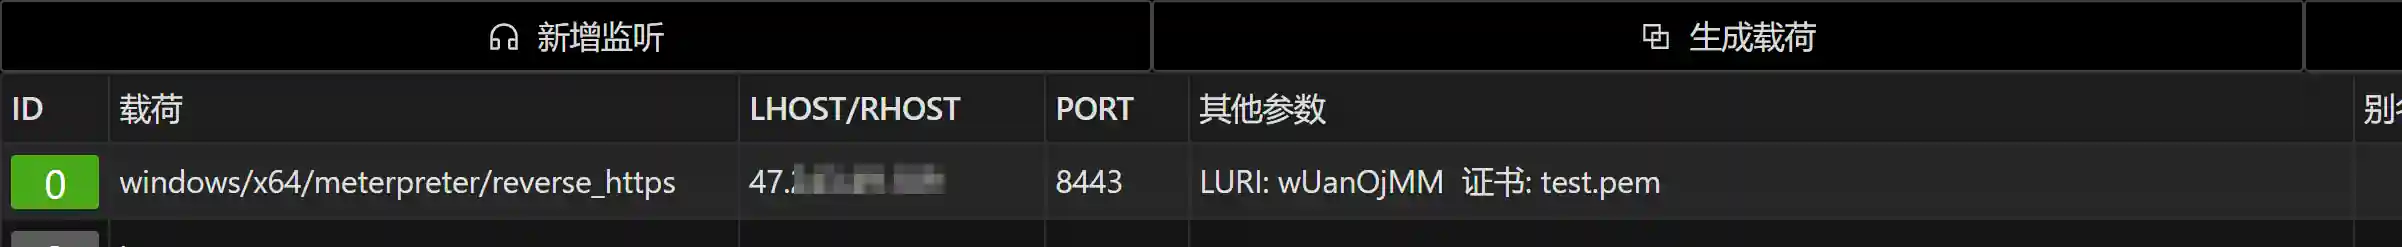
- Use the uploaded pem file to establish monitoring for reverse_https.
- Access the monitoring link. The certificate is already a trusted certificate.